The enterprise AI operating layer.
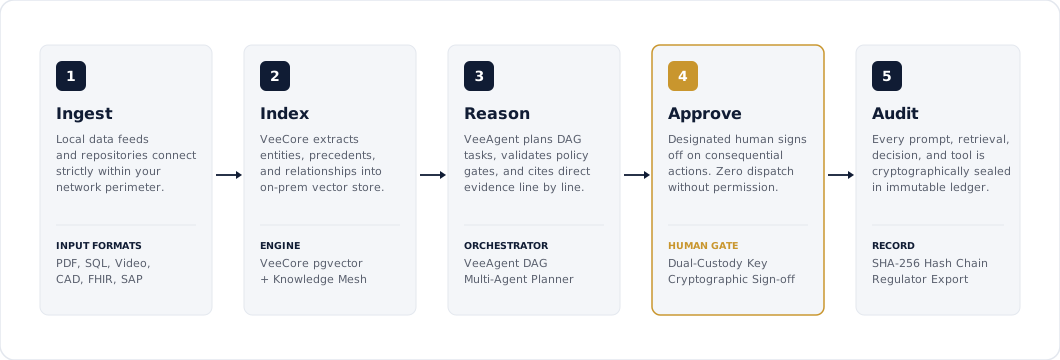
VeeAgent is shared orchestration for every Veebase product: it plans multi-step work, checks policy, and asks a human before acting. VeeCore is its memory. This page describes exactly how data flows — because "trust us" is not an architecture.
Five deterministic stages. Zero cloud leakage.
Deploy anywhere across the spectrum.
Deploy Veebase anywhere across the spectrum — from multi-region cloud to completely isolated enclaves. The software is the same; only the perimeter changes.
| Deployment Mode | Where Data Lives | Who Operates It | Network Requirement |
|---|---|---|---|
| Public Cloud | Dedicated single-tenant VPC | Veebase or Customer IT | Standard outbound HTTPS |
| Sovereign Cloud | In-country region-locked cloud | Certified regional cloud partner | Domestic in-country connectivity only |
| On-Premises | Customer enterprise data center | Customer IT & Security team | Internal network only; zero internet egress |
| Private Appliance | Pre-configured secure hardware server | Customer security staff | Air-gap capable; optional local LAN |
| Tactical Edge | Field-deployable ruggedized unit | Tactical unit operators | Standalone; zero uplink needed |
| Fully Air-Gapped | Physically isolated SCIF / vault | Vetted internal personnel only | Complete physical & electronic isolation |
What we will not do.
- We will not exfiltrate your data. On-premises means on-premises.
- We will not deploy a black box. Every agent run is explainable and auditable.
- We will not let agents execute consequential actions without human approval.
Technical Appendix (For Engineering Teams)
The following describe our architecture design targets and supported protocols:
- Storage & Retrieval: PostgreSQL with pgvector extension for high-performance localized vector similarity search.
- Interoperability Protocols: HL7 FHIR R4 standard connectors for clinical hospital environments.
- Access Governance: Role-based access control (RBAC) with local Active Directory / LDAP synchronization.
- Cryptographic Controls: AES-256 encryption for data at rest; TLS 1.3 for all internal LAN communication.
Technologies We Build On & Integrate With
Veebase is engineered to deploy across enterprise-grade compute platforms, sovereign cloud enclaves, and operating fabrics. The following technologies represent the foundational infrastructure layers, accelerated computing runtimes, and enterprise platforms we build on, optimize for, and integrate with — not commercial reseller partnerships.
NVIDIA
TensorRT-LLM optimization, CUDA acceleration, and Triton Inference Server integration for high-throughput, air-gapped sovereign model execution on NVIDIA DGX and enterprise GPUs.
Ubuntu
Security-hardened enterprise Linux distribution, real-time kernel extensions, and isolated container execution environments for air-gapped tactical and on-premises server clusters.
Microsoft
Azure Confidential Computing enclaves, Entra ID (Active Directory) enterprise identity federation, and hybrid deployment within dedicated government tenants.
Amazon Web Services (AWS)
AWS Dedicated Cloud, GovCloud configurations, AWS Nitro cryptographic hardware enclaves, and localized VPCs ensuring strict zero-egress perimeter boundaries.
Cloudflare
Zero Trust Network Access (ZTNA), WAF perimeter shielding, DDoS mitigation, and domestic boundary gateway control for sovereign institutional web ingress.
Google Cloud
Google Cloud Sovereign Solutions, Google Distributed Cloud (GDC) air-gapped architectures, and hardened GKE on-premises cluster orchestrations.
Oracle
Oracle Cloud Infrastructure (OCI) Dedicated Region, Sovereign Cloud for European/GCC public sector, and on-premises connectors for mission-critical Oracle Exadata databases.
Talk to a human about your institution.
Email [email protected] — a person on our team replies within one business day.